Category: Network news

  • The Network Has a Second Job

    The Network Has a Second Job

    We usually think of fiber-optic networks as infrastructure that carries data. But what if those same networks could also become research instruments for the universities and research institutes we connect?

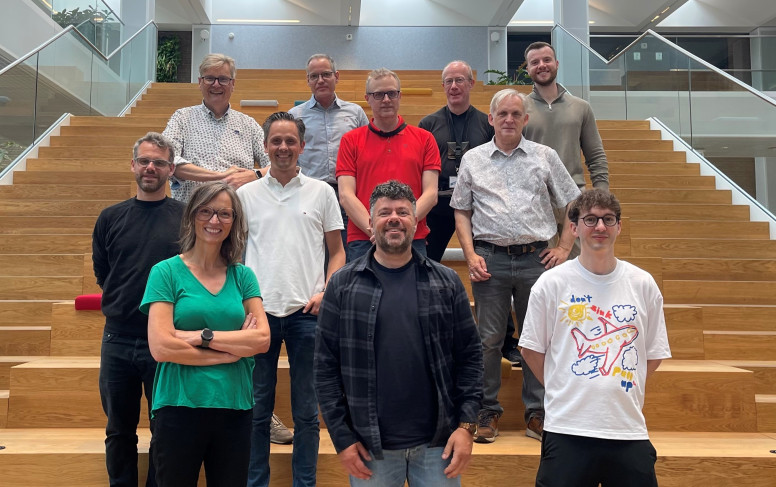
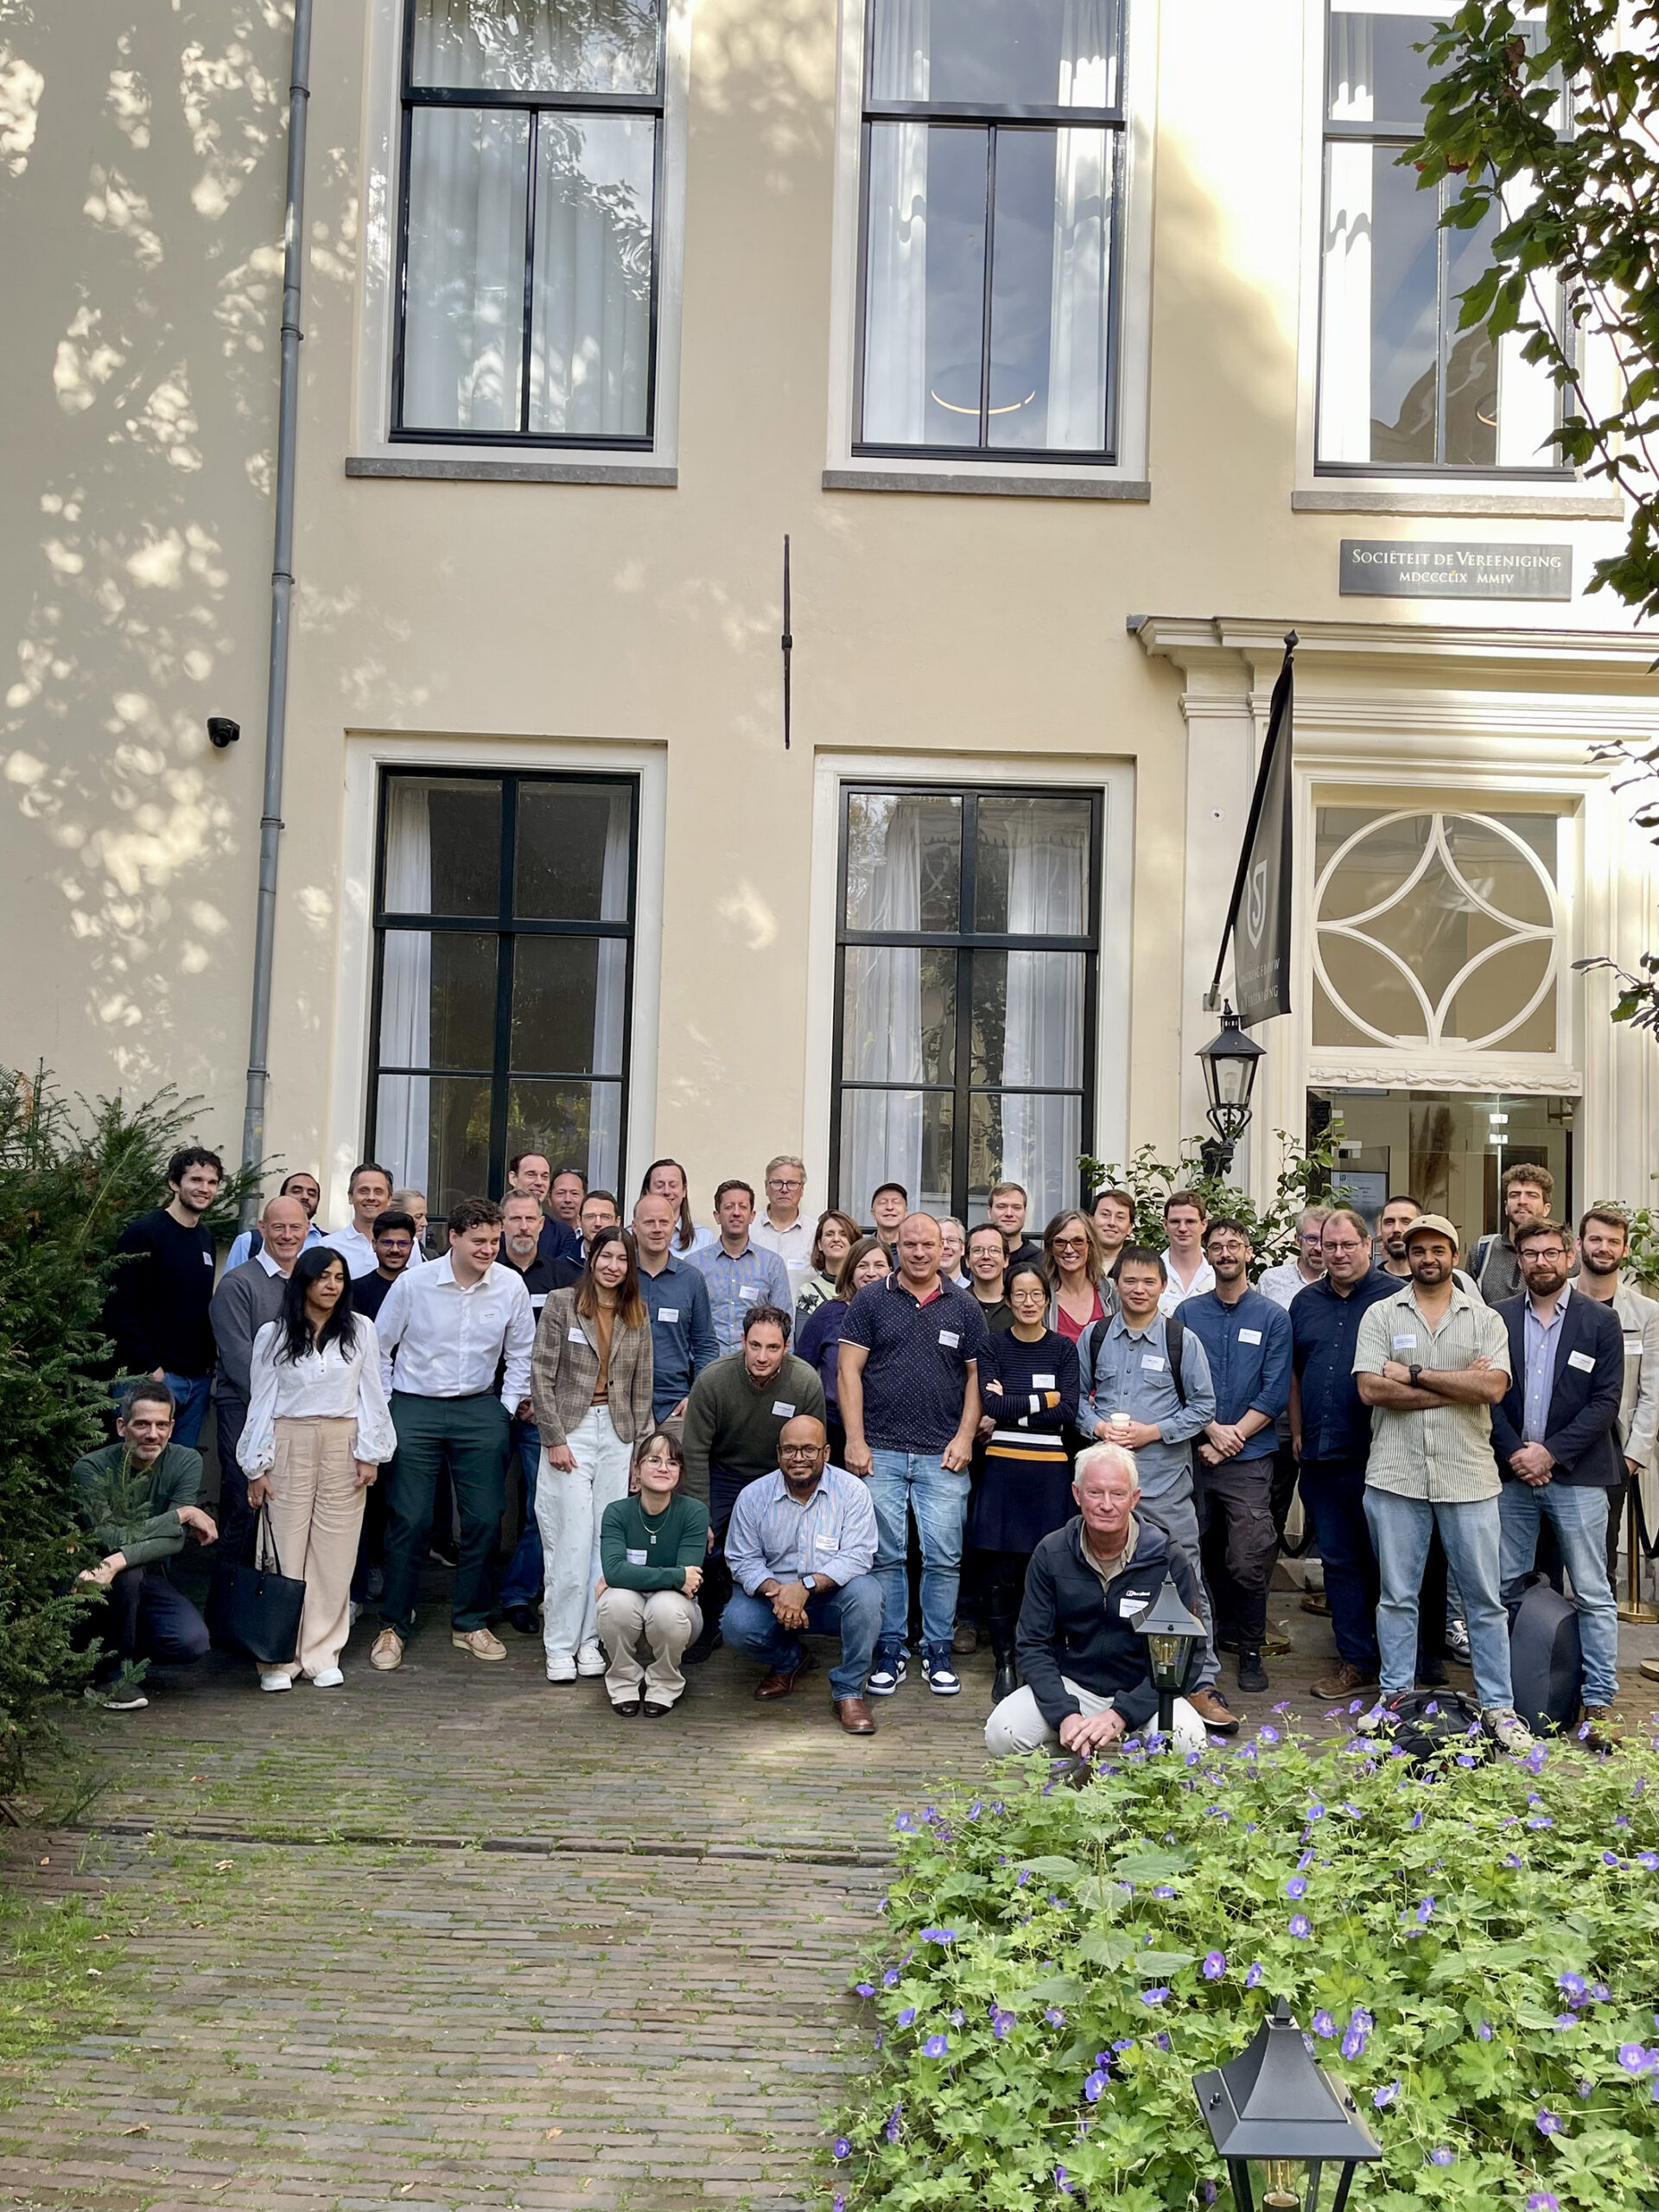
    That was the idea behind SURF’s Fiber Sensing Workshop, held in Utrecht on October 15. We brought together researchers, network specialists, and technology partners to explore how existing fiber-optic infrastructure can be used for scientific observation, and what it would take to make this work in practice.

    SURF has been exploring fiber-optic sensing for some time now, and the workshop was an opportunity to bring that work together with research already happening in the Netherlands and elsewhere. Community-building was a big part of the idea. We wanted people to exchange knowledge, get to know one another’s work, and see where more concrete collaboration might be possible.

    The day opened with an update on fiber-optic sensing activities at SURF, including a technical demonstration and a look at the practical aspects of supporting research, from funding and partnerships to data and computing resources.

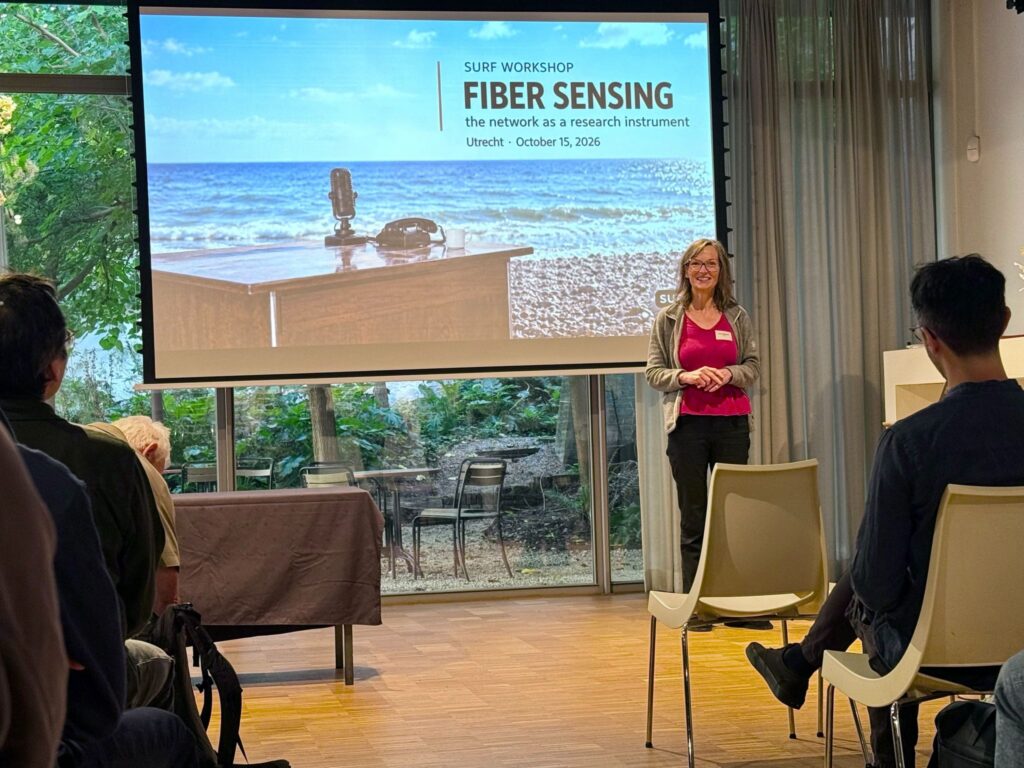
    An international perspective came from Nicolas Celli of the Dublin Institute for Advanced Studies in Ireland. His excellent presentation took us through the use of telecommunications cables as geophysical sensors, covering everything from rain and storms to earthquakes, passing cars, and even quarry activity. It was a fascinating illustration of just how much information can be extracted from fiber infrastructure originally installed for a completely different purpose.

    The research presentations that followed showed a similarly wide range of interests. And the mix of people in the room was impressive: researchers and specialists from TU Delft, Eindhoven University of Technology, the University of Twente, Utrecht University, Vrije Universiteit Amsterdam, Wageningen University & Research, ArtEZ, TNO, Deltares, and KNMI. We also had participants from ProRail, Alliander, and the Dutch police, along with international colleagues from GEOMAR, Jisc, and GÉANT. Quite a diverse group, with research interests ranging from seismic monitoring and urban subsurface investigations to noise in the North Sea, railway infrastructure, geothermal energy, and water safety.

    What I found particularly interesting was seeing how differently researchers can approach the same sensing data, each with their own questions, methods, and objectives. Measurements collected along a fiber-optic cable might contain information that is useful to several research disciplines. It’s an intriguing prospect, especially when you consider the opportunities for sharing data and making more effective use of existing infrastructure.

    And that was perhaps what made this workshop so worthwhile. The presentations were interesting in their own right, but the conversations they sparked were just as valuable. There was no shortage of questions, ideas, or enthusiasm in the room. People were clearly interested in what others were doing, and in finding out where their own research or expertise might fit in. By the end of the day, we had moved well beyond introductions and exchanging information. New connections had been made, possible areas of collaboration had emerged, and there was a shared interest in taking things further.

    For SURF, that’s an encouraging outcome. Our networks have been supporting research for years, mostly behind the scenes, by connecting institutions and carrying their data. Fiber sensing offers an interesting new possibility: the very infrastructure we’ve built to connect our members could also help them generate research data, potentially serving several different disciplines at once. I’m looking forward to seeing which of the conversations started in Utrecht will turn into actual collaborations.

    Interested in learning more about fiber sensing at SURF, have an idea for collaboration, or want to get involved? Feel free to reach out to me at karin.wessel@surf.nl
  • Pixelflut: A weekend of pinging on SURFnet Infinity

    Pixelflut: A weekend of pinging on SURFnet Infinity

    This blog post is a collaboration between Max Mudde, Edwin Verheul and Joachim Opdenakker.


    Network stress test 

    A new network – and, in particular, a wonderful collaboration with Nikhef to host one of the core sites – naturally calls for a festive opening. Read more about it here: https://www.surf.nl/nieuws/surf-brengt-hart-van-netwerk-terug-in-eigen-cooperatie

    But as a techie, you naturally want the technology to speak for itself. In collaboration with Nikhef and Studenten Net Twente, we came up with the idea of routing ‘difficult’ traffic through the SURFnet Infinity network. This allowed us to display some impressive graphs during the ceremony, and afterwards, ‘just for fun’, to open this up to the public as a fun internet event.

    But what exactly constitutes ‘heavy’ traffic? Gigabits? Terabits? Although we usually measure network capacity in bits per second, a router does not operate using bits. A router works with packets. Every packet, large or small, takes roughly the same amount of work: the router has to receive it, look up the destination, check whether the packet is allowed through, update counters and then forward the packet via the correct port. Whether that packet is 64 bytes or 1,500 bytes makes hardly any difference.

    Normal internet traffic is a mix of large and small packets. To account for this, we generally use the concept of IMIX, or Internet Mix. This is a standard distribution of the traffic observed in practice on networks. If you take the average of this, you arrive at an average packet size of 350 to 400 bytes. A connection with a capacity of 400 gigabits per second, carrying IMIX traffic, means that the router has to process around 140 million packets per second. 

    But IMIX isn’t enough, of course; we want to show what the network is capable of. Enter: the pixelflut!

    What is a ‘pixel flut’? 

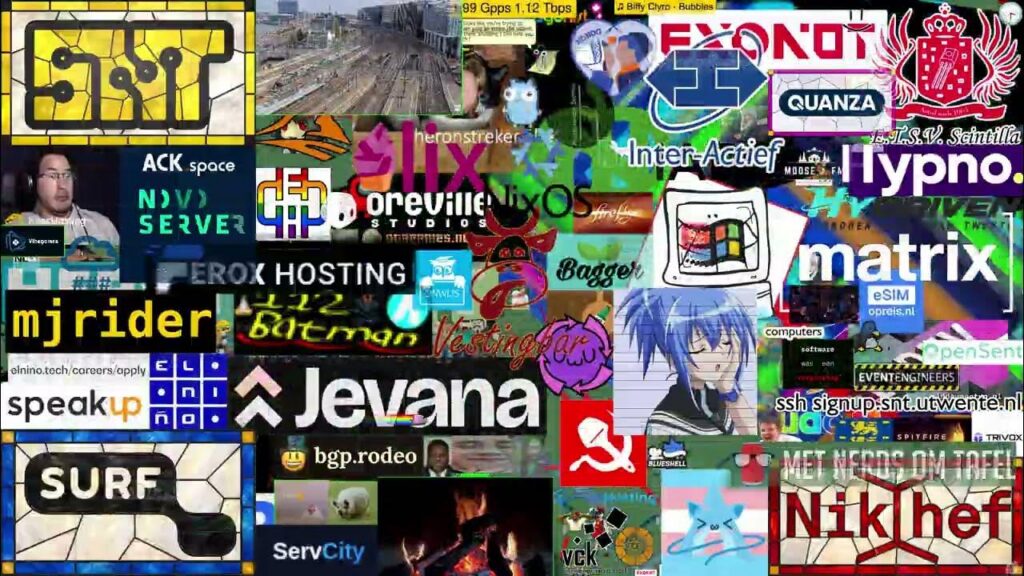
    Imagine a huge digital painting that anyone on the internet can draw on at the same time. There’s no brush or mouse. You draw by sending messages via the internet. Each message colours a single pixel on the screen. You can follow the result live via a livestream. That’s a ‘pixelflut’. The idea comes from the hacker scene and is a regular feature at hacker events. 

    The screen is shared, so anyone can overwrite someone else’s work. If you want your drawing to stay on the screen, you have to keep resending your pixels – and do so faster than all the other ‘pingers’. This creates a fun, chaotic competition. Participants write clever programmes that send as many messages per second as possible. This makes a ‘pixelflut’ an excellent stress test for a network too. 

    What is a ping? 

    A ping packet is just about the smallest packet there is. In this SNT Ping Test, all the information is contained in the destination address, so the contents of the packet can remain empty. To fill that same 400 Gigabit per second connection with such ping packets, the router will have to process around 600 million packets per second. For the same volume of traffic, the router therefore has 4.28 times as much work to do as with IMIX traffic.

    On a ‘normal’ pixel-based chat service, you send text commands to a server. Last weekend’s edition, SNTPings by Studenten Net Twente, works differently: there, you ‘draw’ using pings. 

    A ping is the simplest message you can send over the internet. It works a bit like shouting “Hello, are you there?” in a dark room. Your computer sends a small packet to an address. If that address exists and the device is reachable, a reply comes back. Network administrators have been using ping for decades to check whether a computer or server is reachable and how fast the connection is. Virtually every computer has a built-in ping command. 

    How does a ping become a coloured pixel? 

    The trick lies in the address you send the ping to, not in the contents of the packet. 

    Every device on the internet has an IP address, which is similar to a postal address. The latest version, IPv6, has extremely long addresses. There are so many of them that there is more than enough space to hide information within the address itself. SNTPings makes clever use of this. An address looks like this: 

    2001:610:5ea:221e:<X>:<Y>:<B><G>:<R><A> 

    The numbers are written in hexadecimal, a number system commonly used by computers (using 0–9 and a–f). For example: with 

    ping6 2001:610:5ea:221e:0019:0019:00d1:ffff 

    Colour the pixel at position (25, 25) a bright yellow, in SNT’s corporate colour. 

    With SNTPings, the receiver does not send a reply. It simply reads the address to which the ping was sent, extracts the position and colour from it, and colours the corresponding pixel on the canvas. One ping therefore equals one pixel. The screen is 4K (3840 × 2160 pixels, over 8 million pixels in total). This means that millions of pings are needed for a single complete image, and you have to keep repeating this process as long as others are drawing over it. 

    A whole weekend of gaming on SURFnet Infinity 

    SNTPings was organised to mark the launch of SURFnet Infinity. The event was open to everyone from 6.00 pm on Friday 9 October until Sunday 11 October. It was the biggest edition ever. The receiving servers were located at Nikhef in Amsterdam. SURF and Nikhef together provided 10 × 400 Gbit/s of connectivity, and the receiver itself was capable of processing up to 1.6 Tbit/s of pings. By way of comparison, that is thousands of times faster than a high-speed fibre-optic connection at home. 

    A lot was going on behind the scenes: 

    • SURFnet Infinity router: All traffic first entered via the SURFnet Infinity peering router, an HPE/Juniper PTX10002-36QDD. 
    • Nikhef router: That traffic was forwarded to the Nokia 7750 at Nikhef. 
    • Monitoring: some of the traffic was routed to a monitoring system. This enabled SNT to see who was posting what and, where necessary, to block inappropriate content. 
    • Fair play: anyone with an extremely high ping was artificially assigned a higher packet loss rate. The higher your ping, the greater the proportion of packets that ‘disappeared’ en route. This ensured that even participants with a standard home internet connection had a fair chance. 
    • Drawing: the pings that did get through were sent to the ‘painting server’, which displayed them on the canvas. 
    • Broadcast: a dedicated server streamed the canvas live to the rest of the world. 

    Statistics 

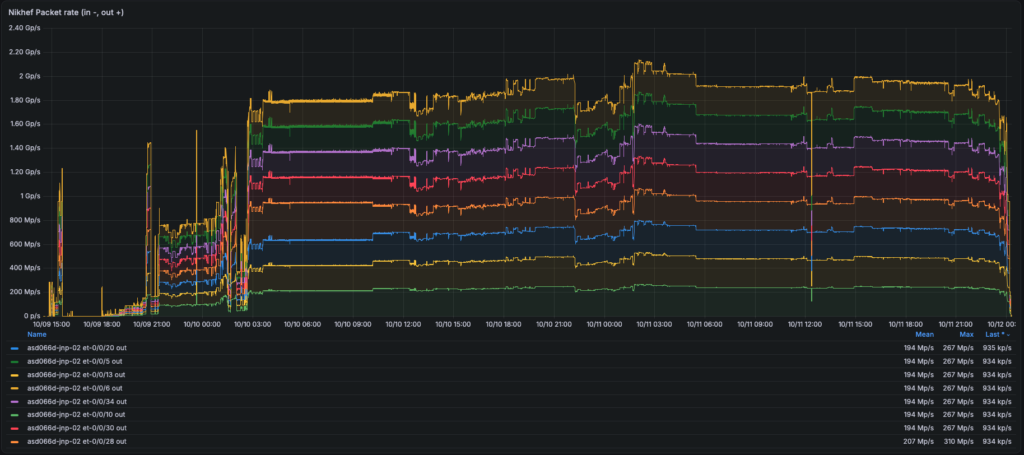
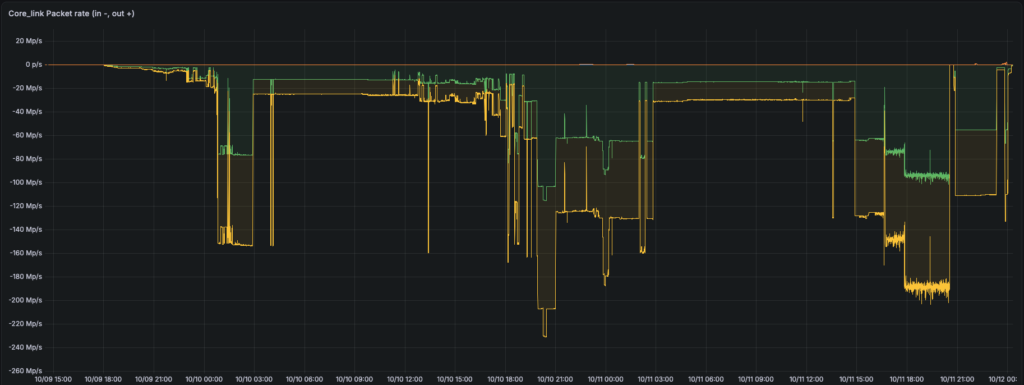
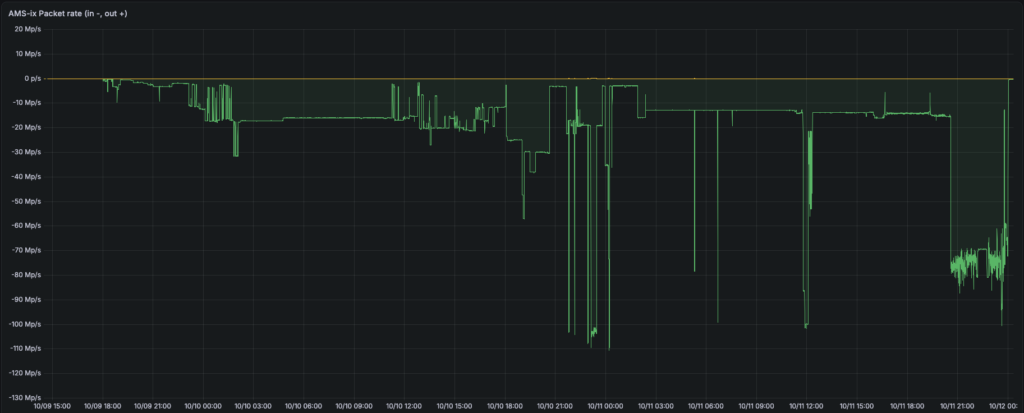
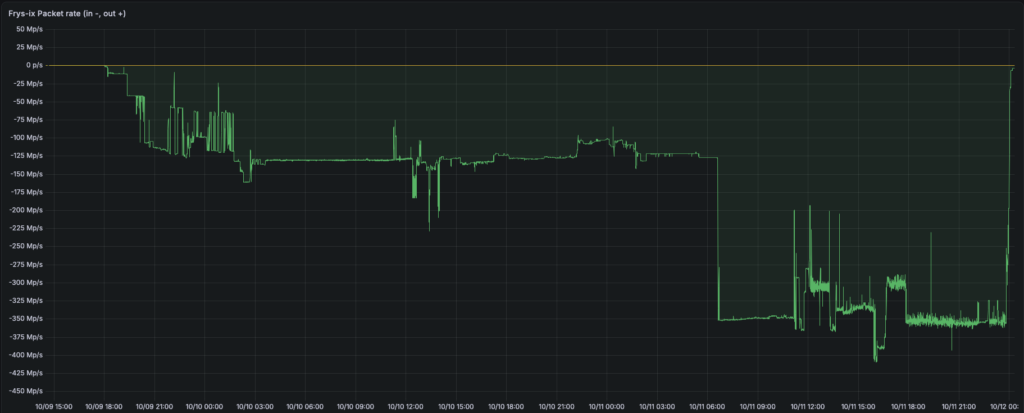
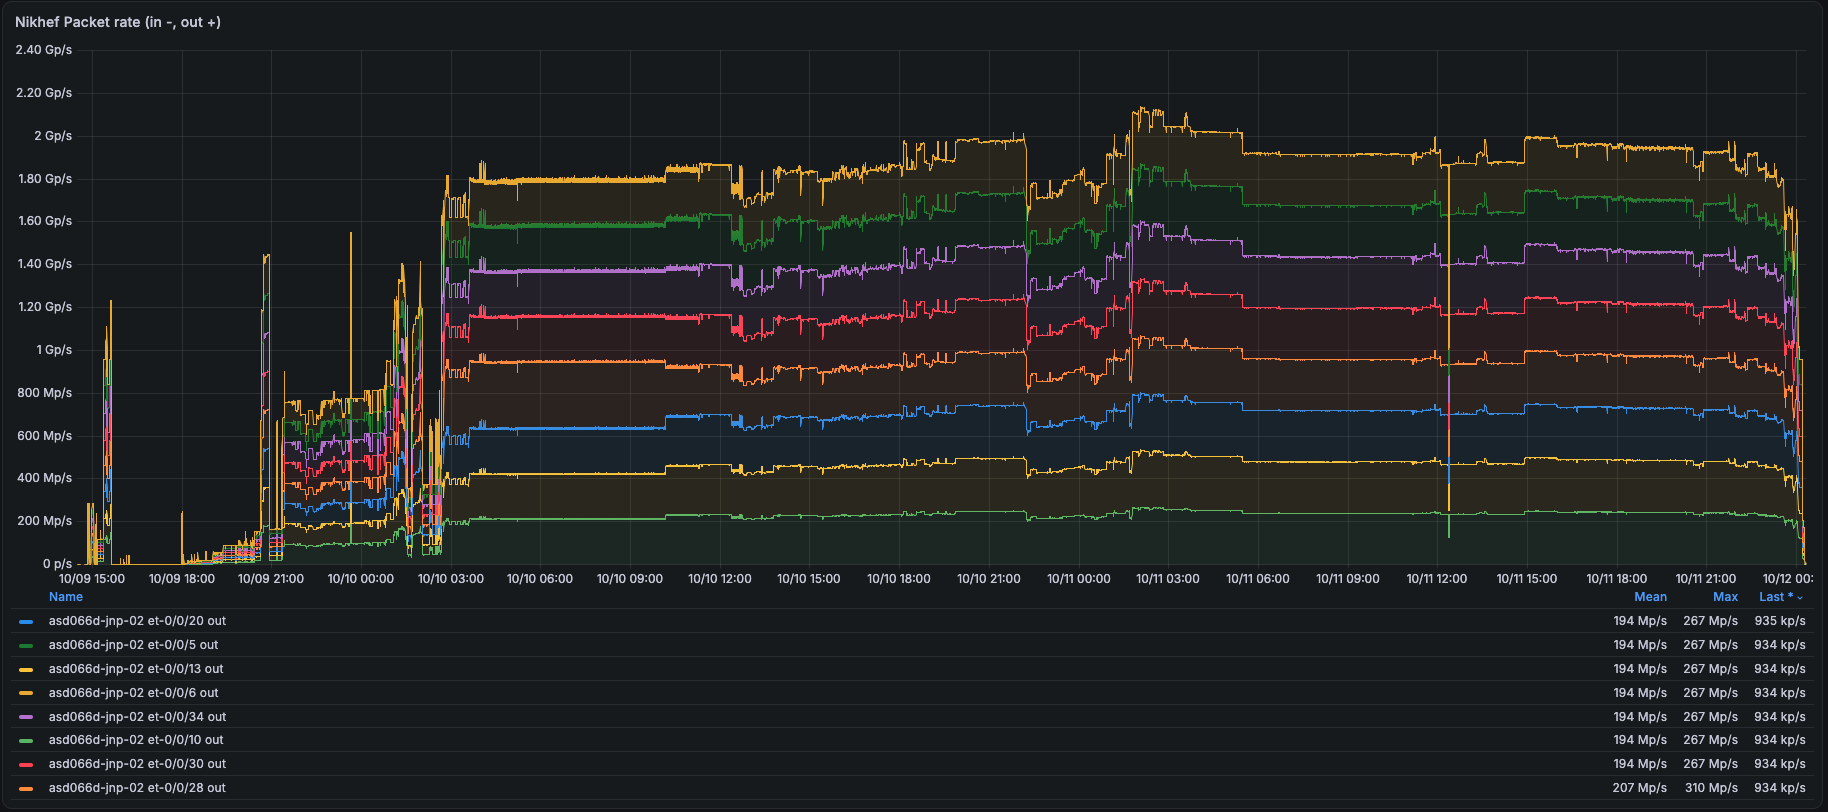
    As you can see from the screenshot below, the maximum parcel throughput peaked in the early hours of Sunday 11 October 2026: no fewer than 2.14 billion parcels per second. This graph shows the 8x400G ports that SURF installed in collaboration with Nikhef.

    Packet rate towards Nikhef/SNT canvas servers.

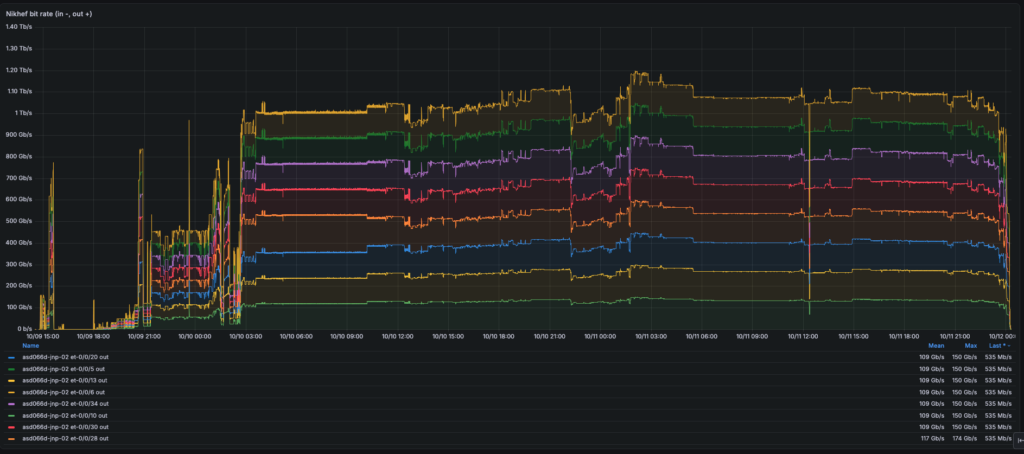
    Below is the resulting bit-rate:

    Bit rate towards Nikhef/SNT canvas servers.

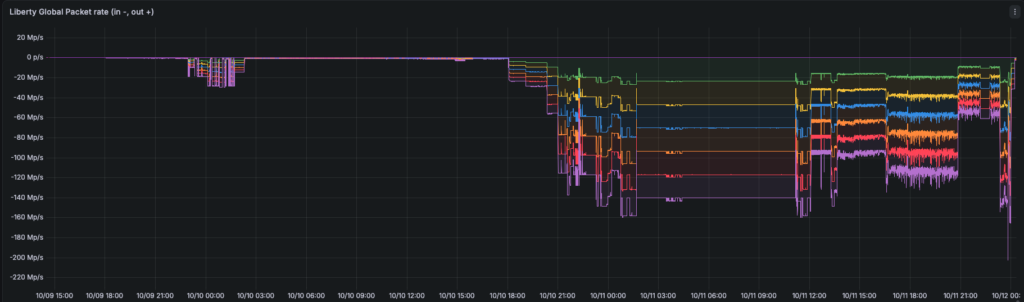
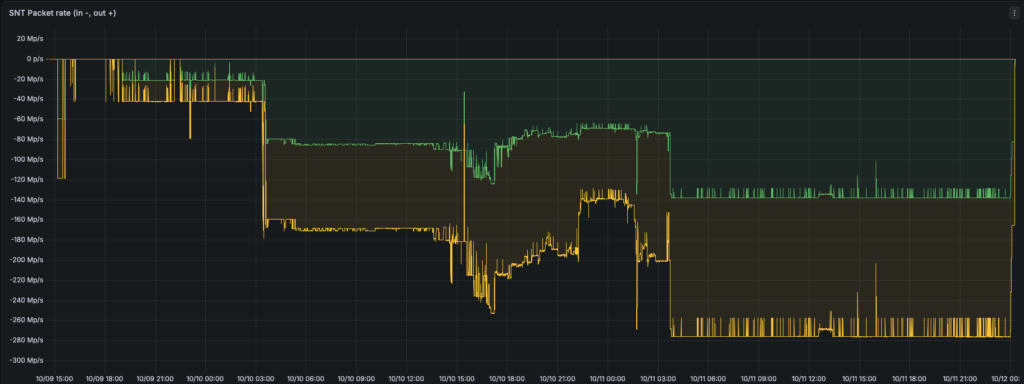
    For incoming traffic, various routes were made available, including a number of internet exchanges, transit providers and, of course, the SURFnet Infinity production network:

    Result

    The result was a weekend full of pixel art, logos and, above all, a great deal of chaos. The best bits can be seen in the time-lapse, which shows the weekend at 200 times normal speed. Meanwhile, the new network proved that it can handle such enormous volumes of traffic without any problems. 

  • Ready for the future with an 800G peering network

    Ready for the future with an 800G peering network

    SURF is building a new generation of the SURF network. This blog is part of a series of blogs about SURFnet Infinity. With SURFnet Infinity, SURF has opted for a vendor-neutral architecture based on open standards, ensuring that the network can continue to develop without restriction. You can read more about the new SURF network here.

    In this blog, we’ll take a closer look at the technology and focus on SURFnet Infinity’s new peering network.

    The first step

    In 2025, SURF organised a mini-competition in collaboration with the broker Nomios. Juniper-HPE emerged as the winner for the core and peering domain with its PTX10000 platform. In addition to the hardware, the anti-DDoS solution used by SURF was also part of this mini-competition. As part of the Juniper-HPE proposal, the new software package from supplier Corero, Corero Smartwall One, was selected. This version has been specifically developed to support Juniper PTX. This new version of the software package offers a clear upgrade path from the existing Corero implementation currently used by SURF.

    Replacement of the peering routers

    In 2025, we quietly carried out a migration of the existing peering routers in the SURFnet8 domain. Until August 2025, all of SURF’s external connections were directly connected to the core routers in Amsterdam. There was a need for greater capacity and increased resilience within the SURF network. As the high-level architecture of the SURFnet Infinity network had already been finalised at that point, we decided to apply the new architecture here for the first time. Dedicated peering routers enable faster capacity expansions, a higher level of resilience in the event of DDoS attacks, and a smaller blast radius. The latter is a key aspect in the separation of network services, as it allows us to significantly limit the impact on other domains.

    In early 2026, we migrated the existing Corero anti-DDoS service to the new package, Smartwall One. This is still linked to the existing Juniper MX-based peering routers, but offers plug-and-play capability for integration with PTX routers.

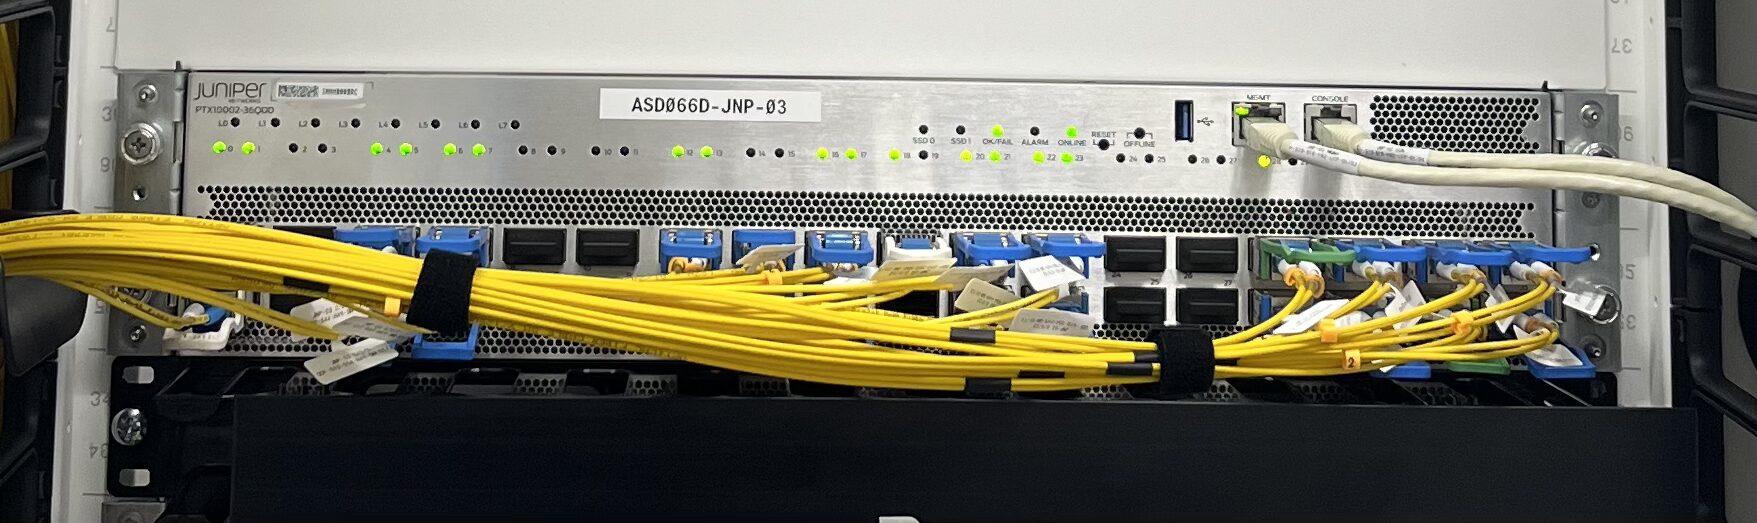
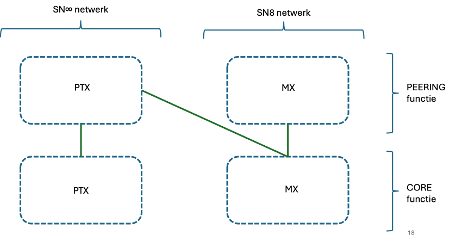
    In July and August 2026, the migration to the new PTX platform took place. New PTX10002-36QDD routers were installed at the main peering locations, Equinix AMS7 and Nikhef. Both routers were provided with direct connections to the new SURFnet Infinity core network, which is currently under construction, as well as direct connections to the SURFnet8 core network. This enables us to gradually migrate customers from SURFnet8 to SURFnet Infinity, with sufficient capacity and without any impact on internet services. By migrating the peering routers ahead of the metro sites and connecting them to both core networks, we can focus fully on migrating the customer sites. There is no need to take routing or capacity into account, as this complex work has already been carried out.

    A diagram is shown below:


    Migration process

    From a bird’s-eye view, such a migration process looks like this:

    • – installation of the new routers
    • – establishing connections with the SN8 core and the SN∞ core
    • – integrate anti-DDoS platform
    • – Migrating the external connections one by one

    This migration was preceded by a major project plan, with the constant aim of causing no impact – or as little as possible – on service delivery. A great deal of planning went into this, particularly at our Nikhef site. Within SURFnet8, one of SURF’s most important peering locations was Digital Realty AMS9. In 2025, SURF decided to relocate the network core to the data centre of one of its members, Nikhef. The Nikhef data centre is one of Amsterdam’s most important connectivity hubs, making it the ideal location for peering. More information about the collaboration: https://www.surf.nl/en/news/surf-moves-network-core-from-private-business-to-member-organisation

    Following consultations with various external parties and peering partners, the necessary cross-connects were requested between Digital Realty AMS9 and Nikhef. This enabled us to connect existing links from parties not physically present at Nikhef to the new peering nodes.

    Field engineers will then migrate all connections from the MX peering router to the PTX peering routers. This means that the optics and fibres will be reconnected on a one-to-one basis. Afterwards, network engineers can use the automation platform developed by SURF to transfer the configuration at the touch of a button. This helps to ensure that the migration proceeds smoothly and without errors.

    Actual migration: a shift in traffic patterns

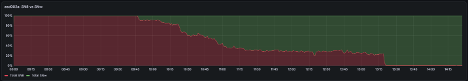
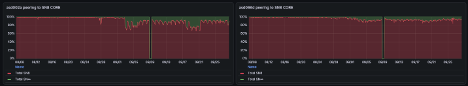
    The actual migration began in the week of 20 July 2026. We opted for a two-stage approach. At the Asd002a site, the migration was carried out using the ‘big bang’ method. On Monday 20 July at around 10.00, the first gateways were migrated to the new PTX platform. The entire migration was completed that same day at around 13.30. The graph below clearly shows the shift in traffic from SURFnet8 peering (in red) to SURFnet Infinity∞ (in green) at the asd002a site.

    Shift in traffic from SN8 MX peering routers (in red) to SN∞ PTX peering routers (in green) at site ASD002A

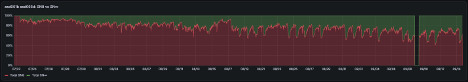
    For the peering migration at site Asd001b, we opted for a phased approach. Various external connections needed to be relocated from site Asd001b (Digital Realty AMS9) to Asd066d (Nikhef). Due to the need to re-establish several campus cross-connects and set up new connections, this migration has been spread over several weeks. We are currently still awaiting the final handover and hope to have fully migrated to the PTX platform at Asd066d by the end of October 2026.

    Shift in traffic from SN8 MX peering routers (in red) to SN∞ PTX peering routers (in green) at location ASD001B/ASD066D

    Distribution of traffic between SURFnet 8 and SURFnet∞

    At present, the migration to the SURFnet Infinity metro network is still well into the design and installation phase. For most customers, this means that internet traffic is still routed via the SURFnet 8 core network. For a small number of metro locations, the migrations to SURFnet∞ have already been completed. We can also already see that traffic from the peering nodes is travelling via the SURFnet∞ core network. This is shown below, where traffic from our peering routers to SURFnet Infinity is shown in green and traffic to the SURFnet 8 core network is shown in red.

    Initial traffic to customers on the SN∞ network (shown in green) by peering location.

    Next step: 3rd peering PoP in Frankfurt

    To make the SURF network even more robust, we have decided to also implement geographical redundancy. As part of the expansion of our Cross-Border network, we are also building a new PoP in Frankfurt. This will enable us to establish external connections here as well, as a fully-fledged part of our peering strategy. The aim is to establish connections with other networks at this location later in 2026, thereby increasing our redundancy and capacity.

    Further information

    Would you like to find out more about SURFnet Infinity?

    Follow this project on this page. We also post regular project updates on the network dashboard. Alternatively, please contact us at joachim.opdenakker@surf.nl

  • SURF tests new White Rabbit feature for picosecond-level timing monitoring

    SURF tests new White Rabbit feature for picosecond-level timing monitoring

    International field trial demonstrates high-precision timing measurements directly from existing White Rabbit infrastructure.

    SURF has successfully tested a new open-source White Rabbit monitoring feature that enables timing differences between network links to be measured with picosecond-level precision directly on White Rabbit switches. The feature was evaluated during an international field trial with SIKT and NORDUnet, using several hundred kilometers of existing fibre infrastructure and SURF’s live DWDM production network. SURF, connected in Hamburg through NORDUnet to the Nordic Timing Pilot.

    The new functionality extends timing monitoring beyond the traditional upstream White Rabbit link. It makes it possible to monitor additional links, redundant paths and multiple timing sources directly from the White Rabbit infrastructure.Because the measurements are performed by the White Rabbit switches themselves, no additional dedicated measurement equipment is required for the monitoring function. This reduces both cost and operational complexity, particularly in distributed timing networks.

    Comparing national time scales

    During the field trial, White Rabbit switches running a beta version of the new firmware were used as part of a comparison between the time scales of VSL, the National Metrology Institute of the Netherlands, and RISE, the Swedish National Metrology Institute.

    The trial demonstrated that the new functionality can perform picosecond-level timing monitoring in an operational network environment.The basis for the feature was originally developed by VU Amsterdam. SURF is working with its member institutions to bring research innovations into operational networks.

    The White Rabbit Collaboration Bureau is now preparing the functionality for inclusion in a the latest version of the official release of the open-source White Rabbit Switch firmware. As a member of the White Rabbit Collaboration, SURF contributes by testing new developments in operational network environments and providing practical experience to the wider White Rabbit community.

    “By performing these measurements directly on the White Rabbit switches, we can monitor timing differences with picosecond-level precision without additional dedicated measurement equipment,” said Paul Klop, Optical Network Architect at SURF. “The same approach can be used for individual links, redundant paths and larger distributed timing networks, making high-precision timing monitoring simpler and more cost-effective.”

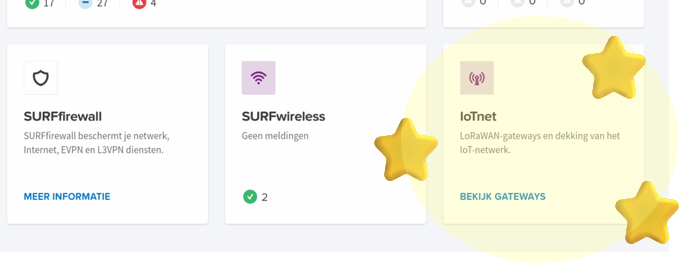
  • IoTnet is now also available in the Network Dashboard

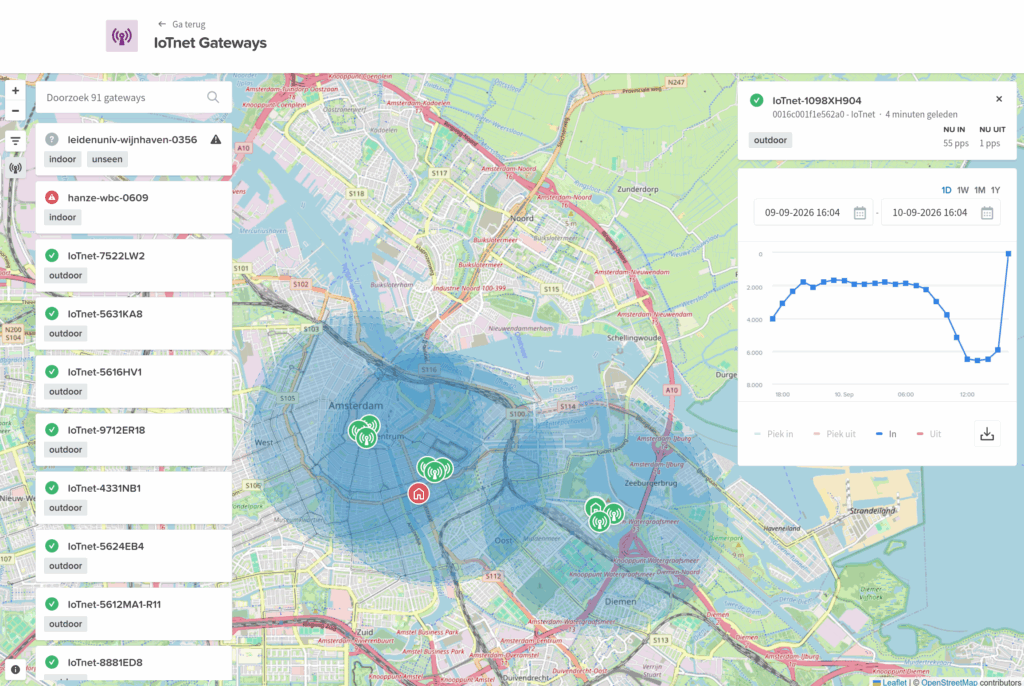
    IoTnet is now also available in the Network Dashboard

    IoTnet, a service currently under development by SURF, provides our members with a wireless infrastructure for sensors based on LoRaWAN. As part of the pilot phase, outdoor gateways have been installed throughout the country for this purpose. Indoor gateways have also been installed for individual institutions. Indoor and outdoor gateways are now accessible via the Network Dashboard, SURF’s customer portal for network services.

    All organisations and users with access to the network dashboard can view the outdoor gateways. Network administrators can see which gateways are located in their vicinity and what their status is. They can also analyse how much traffic has passed through them recently. If organisations manage indoor gateways as well as outdoor gateways, these are also displayed.

    For example, organisations use IoTnet to collect temperature, humidity or CO₂ readings from climate sensors. This enables them to monitor air quality. Motion sensors are also used to detect no-shows in halls, whilst people counters are used to count the number of people in a room. Furthermore, researchers utilise various sensors to measure soil moisture and temperature, or water conditions.

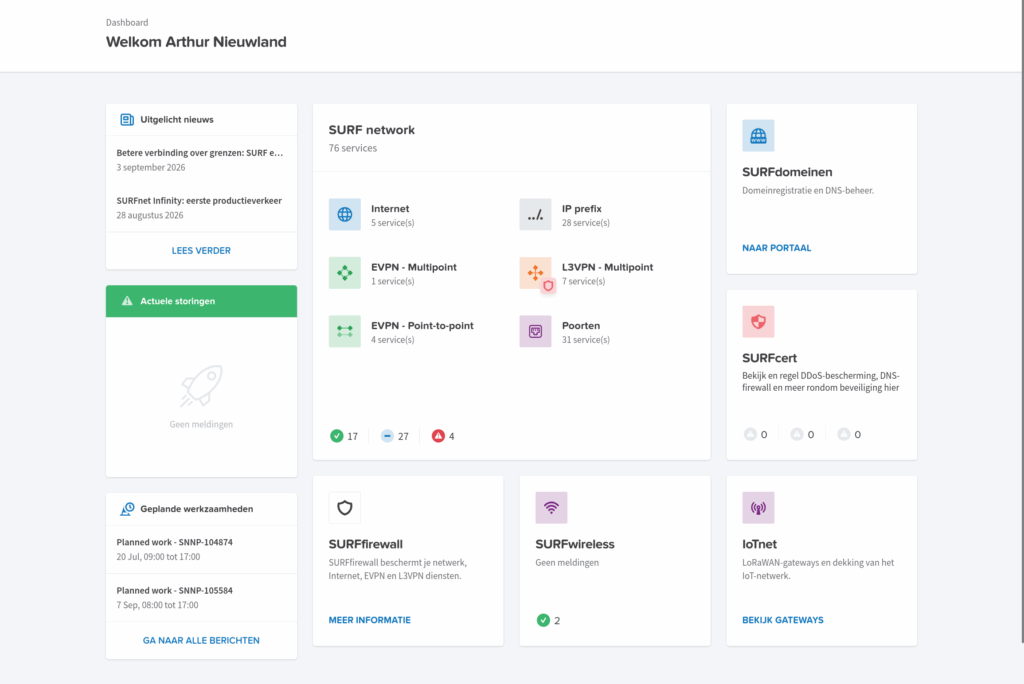
    The Network Dashboard is the portal where administrators can view the status of services. This includes current availability, SLS statistics, traffic graphs and maintenance notifications. Furthermore, for the past year, the SURF Domains service has found a new home there for domain registration and zone management. SURF’s support in the event of cyber-attacks, provided by SURFcert, is also available via the network dashboard.

  • Researchers! Could the fiber network itself become a new research instrument for your field?

    Researchers! Could the fiber network itself become a new research instrument for your field?


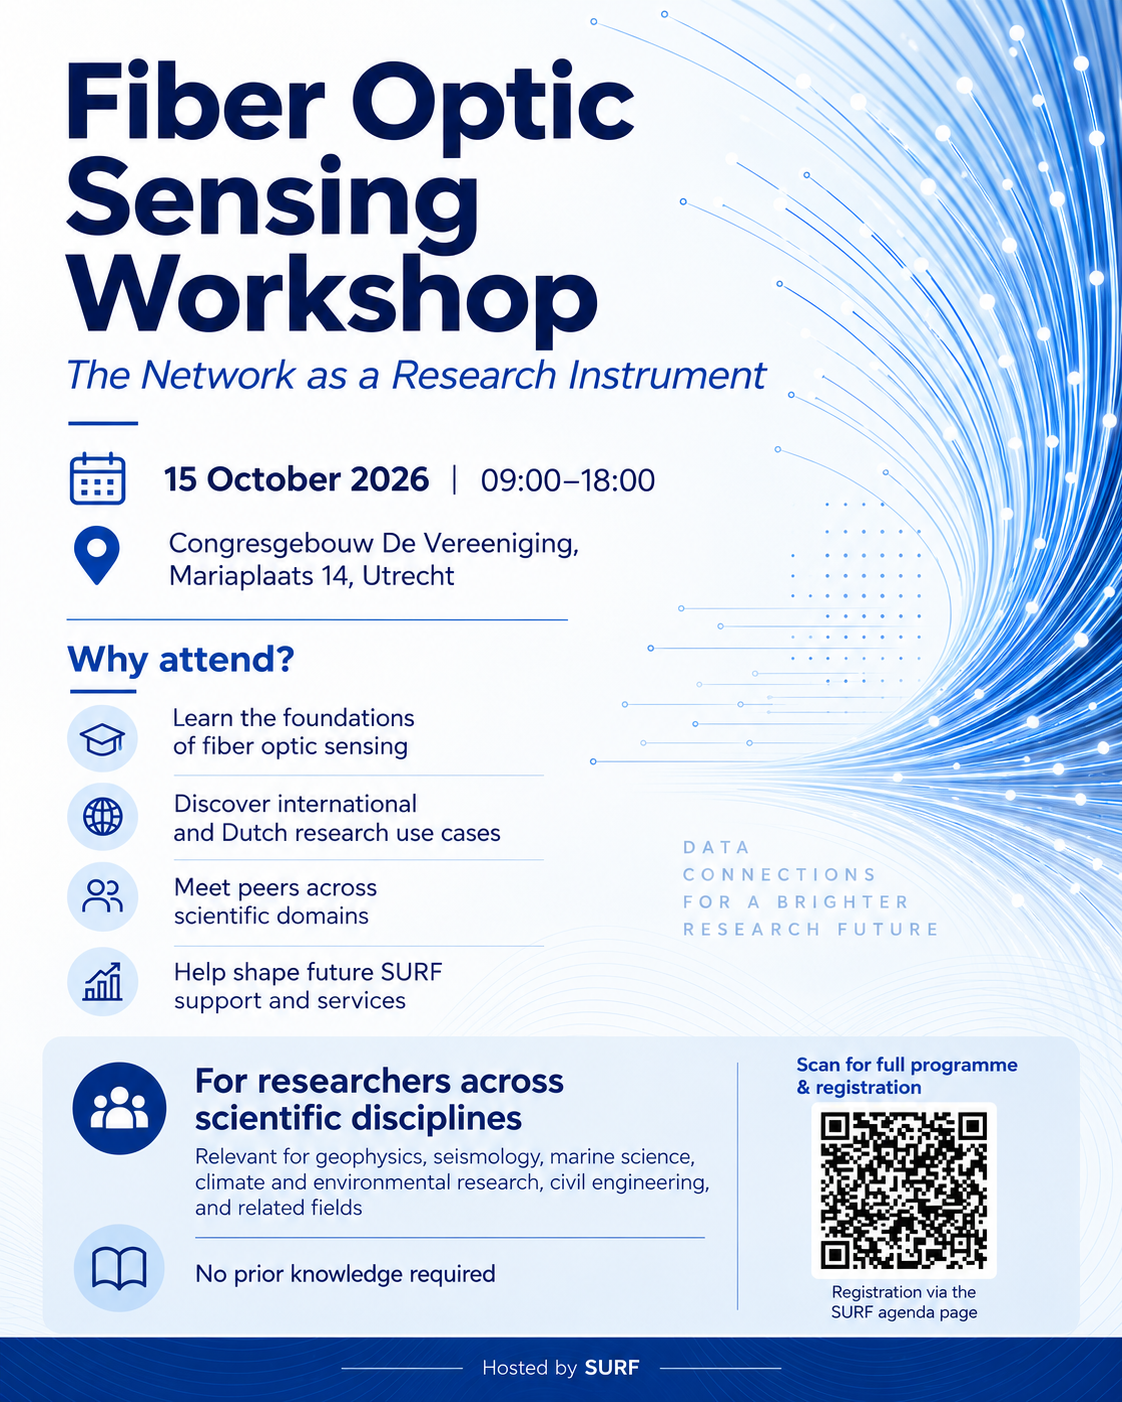
    On Thursday 15 October, SURF is bringing together researchers from different scientific disciplines for a one-day Fiber Optic Sensing Workshop in Utrecht.

    We are particularly keen to connect with researchers whose work could benefit from using existing fiber infrastructure as a distributed sensing instrument — for example in geophysics, seismology, marine science, environmental and climate research, civil engineering, and related fields.

    The focus of the workshop is very much on the science and the research use cases. What can technologies such as Distributed Acoustic Sensing (DAS) make possible? What kinds of measurements, coverage and data could be valuable to different disciplines? And what would researchers need from fiber sensing infrastructure if we want to move from individual experiments towards more structural and scalable research capabilities?

    The day will combine an introduction to the technology with international and Dutch research examples, ongoing projects, discussion across scientific domains, and short pitches from researchers who would like to explore or share a potential fiber sensing use case.

    We will also have a live demonstration with a DAS unit and look at the wider research landscape around fiber sensing, including funding opportunities, consortia and collaboration, and how SURF’s data and compute infrastructure could support this type of research.

    Previous experience with fiber sensing is not required. We are just as interested in researchers who are curious whether this could provide a useful new source of data for their work.

    If this sounds relevant to your research — or to someone in your research network — please have a look and feel free to share.

    Fiber Optic Sensing Workshop: The Network as a Research Instrument
    Date: 15 October 2026
    Place: Utrecht, the Netherlands
    Language: English


    To sign up, please use the registration tool under this link:

  • Better cross-border connectivity: SURF and Germany’s DFN join forces

    SURF and DFN, Germany’s national research and education network, are now sharing optical spectrum via fibre-optic infrastructure across national borders. For SURF’s member institutions, this means greater flexibility in international connectivity. This facilitates access to shared research facilities and the exchange of large volumes of data across borders.

    By exchanging two sets of routes, SURF and DFN are strengthening cross-border connectivity between the Netherlands and Germany and making more efficient use of the infrastructure already available within the research and education community. In a broader sense, the agreement is a building block in a larger European and global ecosystem of research and education networks. Its strength lies in federated collaboration: bilateral, regional and pan-European initiatives reinforce one another.

    Spectrum sharing: independence on shared routes

    The collaboration between SURF and DFN is based on spectrum sharing. As each organisation is permitted to operate its own optical equipment on shared routes, this model combines the efficient use of existing physical infrastructure with operational independence. For NRENs such as SURF and DFN, this provides an important foundation for strong, flexible and future-proof connectivity across borders.

    Connections remain available at all times

    By sharing spectrum, the two NRENs make part of the optical spectrum on their fibre-optic routes available to each other, whilst each network retains control over its own optical network equipment. Under the agreement, SURF provides access to the Amsterdam–Hamburg and Amsterdam–Aachen routes, whilst DFN provides access to the Hamburg–Frankfurt and Frankfurt–Aachen routes. For SURF, the increased route diversity means that Frankfurt can serve as a backup location for internet connectivity, thereby strengthening the resilience of the SURF network. For DFN, Amsterdam also offers an advantage: it adds an extra location for international connectivity, thereby further enhancing the network’s flexibility.

    A cross-border fibre-optic strategy

    Ensuring and expanding access to European and global research infrastructure is a key part of SURF’s fibre-optic strategy, which extends beyond national borders. By working directly with neighbouring NRENs on shared routes and capacity, we strengthen our international network whilst retaining control over the infrastructure and equipment that are essential to our services.

    Federal cooperation in Europe and beyond

    The agreement complements connections with other national research and education networks, including partners in the Scandinavian countries via NORDUnet, and the pan-European GÉANT network. NRENs take responsibility for national infrastructures and communities, whilst collaborating across borders on shared capacity, interoperability, innovation and trust. GÉANT plays a key role as a pan-European connector and facilitator within this federation, linking European NRENs with one another and with research networks worldwide.

    Cost-effectiveness

    The collaboration also contributes to cost-efficiency. Rather than building or purchasing each international connection separately, SURF and DFN make better use of the infrastructure already in place within the research and education community. This ensures that the infrastructure remains in shared use and creates scope for innovation, experimentation and capacity expansion in the future.

    A strong digital hub in Amsterdam

    DFN has installed networking equipment at Nikhef, close to NetherLight, SURF’s Global Exchange Point for research and education. Together, this strengthens Amsterdam’s role as a digital hub, connecting Dutch research and education with European and international partners in the fields of science, education and innovation.

    Are you interested in our international network?

    Would you like to find out more about spectrum sharing, cross-border connectivity or SURF’s international network strategy? Please contact Karin Wessel: karin.wessel@surf.nl .
  • SURFnet Infinity: first production traffic

    SURF is building the next generation of the SURF network: SURFnet Infinity. The first production traffic was routed over SURFnet Infinity on August 7. The first metro nodes have been installed in Breda, and the initial access rings have been migrated from SURFnet8 to SURFnet Infinity—the latest generation of the SURF network. Our colleague Max Mudde previously wrote an article about this. We shared an initial update in early June, which you can read here.

    Work continued steadily throughout the summer, so time for a new update from the project team.

    The core is in place

    The core network was accepted on August 5. This followed a month of “soaking tests” involving continuous test traffic and simulated outages on the new core, as well as a reconfiguration of the network around Utrecht to provide extra redundancy for fiber-optic routes. The core and peering routers (HPE PTX10008) are now operational at the four core locations and two peering locations, interconnected by 400G links.

    First metro location live

    On August 6, the metro nodes were installed at Avans University of Applied Sciences in Breda. A day later, around 10:30 AM, the first access rings switched over to SURFnet Infinity. On-site access connections will follow in September.

    What’s next

    •          Migration of internet exchanges and direct peers to the new peering routers is 50% complete; finalization is scheduled for the end of August.

    •          The remaining metro locations will follow—a total of 55 locations across the Netherlands.

    •          In the autumn, we will bring the SURFnet Infinity route reflectors online and phase out the SURFnet8 ones.

    •          Next up is the migration of NetherLight, our international exchange point.

    Want to know more?

    See this video! Or read SURFnet Infinity: approach and first steps to learn how the migration is structured. Technical blogs detailing the setup of the new network will follow in the coming months.

  • SURFnet Infinity: approach and first steps

    SURF is building the new generation of the SURF network: SURFnet Infinity. The successor to SURFnet8. Previous generations, from SURFnet1 through SURFnet8, were heavily defined by the choice of a single network vendor. With SURFnet Infinity, SURF is opting for a vendor-independent architecture based on open standards, so that the network can continue to evolve without restriction: hence the name Infinity, and not SURFnet9.

    Technical Product Manager Max Mudde previously wrote this article about it.

    In this article, you can read how the migration project was set up, what is happening now, and what steps will follow.

    What we already did

    Last year, we made two important decisions regarding the configuration of this new network. HPE was selected for the backbone and border domains, and Salumanus for the optical transceivers. Construction is now beginning: the core, IP peering, and metro sites. The optical layer and access sites will follow at a later stage.

    What is happening now

    Through July 2026: construction of new core

    The core of the new network is being built at four new core locations: Delft, Eindhoven, Amsterdam, and Zwolle. During the same period, we are implementing redundancy on the fiber optic routes between these locations, ensuring that every core location is fully redundantly connected to the other three.

    This construction is proceeding entirely parallel to the existing SURFnet8. There is no impact on current services.

    From July 2026: IP peering migration

    Starting in July, we will transfer IP peering—SURF’s external internet connectivity—to the new network. To do this, we will install new peering routers that will be redundantly connected to both SURFnet8 and the new network. Subsequently, we will migrate the peering functionality in phases from the current SURFnet8 routers to the new routers.

    From September 2026: metro locations migration

    Starting in September, we will migrate the metro locations step by step. At each location, we will install two new routers: one router that will be redundantly connected to two core locations and to which the access rings will be linked, and one router to which existing access ports will be migrated.


    Impact on members

    The development of the new core has no impact on service delivery.

    The migration of the metro locations requires slightly more effort: during the work, access rings and access ports will be temporarily interrupted and subsequently connected to the new hardware. As a result, institutions will temporarily have less redundancy, while service delivery remains available.

    The result is a connection to a network with higher capacity, better fault isolation, and more flexibility for future upgrades.

    Each member will receive its own ticket prior to the work, containing an explanation of the schedule and the expected impact.


    More information and updates

    All project information regarding SURFnet Infinity can be found on the project page on the wiki. More project updates and a number of technical blogs regarding the setup of the new network will follow in the coming months.

  • Fiber Optic Sensing Workshop The Network as a Research Instrument 

    Thursday, October 15, 2026 | 09:00 – 18:00

    Congresgebouw De Vereeniging, Mariaplaats 14, 3511 LJ Utrecht, Netherlands

    Costs: Free

    Join us for a cross-domain workshop in Utrecht focused on the future of fiber optic sensing. This event highlights a sophisticated evolution in infrastructure: leveraging the fiber infrastructure itself as a large-scale, distributed research instrument. 

    The program is designed to provide both a technical foundation and a look at what’s possible. We will start with a high-level overview of the underlying technology, followed by concrete use cases and results from various scientific disciplines. Together, we will discuss the transition from experimental pilots to a structural, scalable research infrastructure that serves the entire Research & Education community.

    A key goal of the day is to identify the specific needs of researchers and stakeholders to shape SURF’s future support and digital services in the field of fiber optic sensing.  It’s a great opportunity to socialize, meet peers from different domains, and continue the conversation in a more informal setting. We wrap up the day with drinks. 

    Registration Policy: To ensure a high-quality, interactive dialogue, seats are limited and registration is subject to approval. 

    We welcome a diverse mix of participants: from experienced experts who have already conducted fiber sensing trials to researchers and technical leads who are curious about how this technology could benefit their future work.

    AGENDA (preliminary)

    09:00-09:30 | Registration & coffee

    09:30-10:00 |  Introduction & Opening

    10:00-11:00 |  High-level overview of fiber optic sensing technology & demo

    11:00-11:30 |  Break

    11:30-12:30 |  International use-cases and results from various scientific disciplines

    12:30-13:30 |  Lunch

    13:30-15:00 |  Current projects in the Netherlands

    15:00-15:30 |  Break

    15:30-16:30 |  Pitches for fiber optic sensing use cases by workshop participants

    16:30-18:00 |  Drinks

    Registration Link:

    https://event.surf.nl/fiber-sensing-conference-the-network-as-a-research-instrument/registration

    For further information, please contact karin.wessel@surf.nl